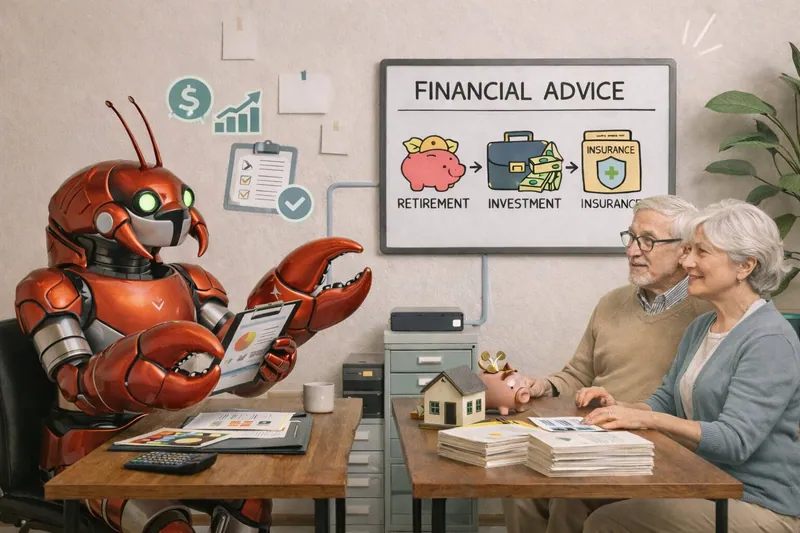
Every advice team already has shadow AI, whether the policy admits it or not. The agent wave is already inside the advice process. The only question that matters now: can you trust and evidence it?
The meeting starts before you walk into it
A growing number of clients are walking into reviews with:
an AI-generated retirement plan
an “optimised” investment switch recommendation
a list of product comparisons and fee breakdowns they didn’t create themselves
a draft email that reads like it came from a paraplanner
This changes the dynamic.
You’re no longer starting from a blank page. You’re starting from a pre-loaded narrative that may be persuasive, plausible, and completely wrong. And it forces a decision on your side:
Do you respond with ad hoc, one-off AI usage to keep up?
Are Cowork-style AI agents enough for advice firms?
There’s a class of “desktop agent” products emerging (Claude Cowork is the latest example) that bring agentic capability to non-technical work: local files, connectors, browser actions, task delegation. It’s a meaningful step toward autonomy, and Anthropic positions it as a research preview with explicit permissioning to folders/connectors you choose.
But here’s the catch,
Giving advisers an AI coworker and expecting transformation is like giving everyone Excel and expecting operational excellence.
Excel is powerful. But itdid not magically create a scalable back office.
Tools don’t deliver outcomes. Systems do.
Most “AI coworker” setups today are still:
single-player (one person, one screen, one session)
interface-driven (clicking and prompting)
outcome-agnostic (no enforced standard, no review gates, no audit posture)
That can help an individual adviser move faster.
It does not, by itself, create a governed advice operation.
OpenClaw shows the potential, and the warning label
Open agent ecosystems (OpenClaw is the trend symbol right now) show what people actually want:
a system that can take a goal and complete a workflow
a marketplace of skills
multi-step autonomy
integrations that do the doing, not just draft the words
That “shape” is the future.
But the same open marketplace dynamics that make these ecosystems explode also make them messy in the short term. Recent reporting has highlighted how an open “skill” model can become a permissions and security problem when extensions are user-submitted and the agent can read files or execute actions.
In other words: OpenClaw is showing the endgame. It’s also showing why regulated industries can’t just copy-paste the consumer playbook.
The enterprise takeaway is not “agents are unsafe.”
The takeaway is: permissioning, assurance, and governance are not optional features.
They are the product.
Are advice firms already using unofficial AI agents?
Whether you call it “shadow AI” or “getting things done,” the pattern is already familiar:
text gets pasted into random tools to tidy wording
meeting outputs get summarised outside approved systems
someone tests an automation that quietly touches client data
drafts float around without a clean record of how they were produced
That pattern is not anecdotal. A 2025 workplace AI study by Zluri found that about 80 percent of enterprise AI apps in use were unmanaged, meaning they sat outside formal IT control. (businesswire.com) IBM’s 2025 Cost of a Data Breach work goes further: about one in five organisations surveyed had already suffered a cyberattack linked to shadow AI, and those breaches cost on average 670,000 US dollars more than incidents at firms with little or no shadow AI. (IBM Newsroom)
Bans don’t fix this. They usually just push it further underground.
The practical implication is uncomfortable:
You cannot stop AI usage. You can only decide whether it is governed or a free for all.
How are small advice firms rebuilding their back office with AI?
The “edge” of the market moves first.
Right now, smaller advice businesses are experimenting with something bigger than note summaries. They’re trying to replace large parts of their operating model:
intake → meeting → file note
file note → paraplanner brief
brief → SOA sections
SOA → review checks
review → delivery pack
delivery → follow-up tasks and client comms
The speed is real. The risk is also real.
Because if every step is powered by different tools, different prompts, and different versions of “how we do it here,” you don’t get leverage. You get inconsistency, and a record-keeping problem that only shows up when something goes wrong.
The future isn’t one magic agent. It’s a controlled system of agents with review gates.
This is the core mistake most teams make when they think about agents:
They imagine one super-agent doing everything.
Advice doesn’t work like that.
Advice is a chain of artefacts, handoffs, checks, and accountability. So the useful model is not “one agent.” It’s a governed system of specialised agents, each with:
a defined role
limited permissions
standardised outputs
audit trails
review gates
That is what “governable agents” actually means in practice.
What an advice-grade agent workflow looks like
Here’s the pattern that matters for most firms:
Meeting → SOA → Queries / Complaints
Not as a demo. As an operating system.
1) Capture agent (meeting to working record)
Purpose: turn raw conversation into a usable internal artefact.
transcript is input, not the record
file note is standardised, predictable, and skimmable
key decisions, rationale, risks, next steps are extracted in the same structure every time
This is the difference between “we recorded it” and “we can run the case forward.”
2) Drafting agent (record to SOA building blocks)
Purpose: draft the parts that normally bottleneck.
strategy sections drafted against your firm’s structure
house language, disclaimers, and formatting applied by default
content is produced as components that can be reviewed and assembled, not one giant blob
3) Verification agent (consistency and integrity checks)
Purpose: catch the failures that create rework, risk, and complaints.
checks for data conflicts and inconsistencies
flags gaps in rationale or missing elements
highlights where the story doesn’t match the file
This is where most “AI everything” stacks fall apart, because they optimise for drafting, not for assurance.
4) Compliance / review agent (rule alignment and risk gating)
Purpose: reduce back-and-forth and make review faster.
applies firm policies and checks alignment against regulatory expectations
flags issues early, before it becomes a rewrite cycle
If AI is acting inside core workflows, control has to rise dramatically, especially once the system starts doing more than drafting.
5) Service agent (post-advice reality)
Purpose: handle the part the industry underestimates.
Because after delivery, the work continues:
client questions
implementation clarifications
file maintenance
and sometimes: complaints
A governed service agent helps ensure:
responses remain consistent with the advice record
supporting artefacts are easy to assemble
the file stays coherent over time
This is where a firm either looks professional and controlled, or chaotic and improv-based.
The advice-grade agent checklist
Before you let any agent touch client data or advice artefacts, ask:
Permissioning: What can it access? What is explicitly blocked?
Standardisation: Are outputs templated, or “whatever the model felt like today”?
Verifiability: Can you trace outputs back to sources and inputs?
Audit trail: Can you see what it did, when, and why?
Review gates: Where must a human sign off before anything leaves the building?
Sovereignty: Where is data stored and processed, end-to-end?
If you can’t answer those cleanly, you don’t have an agent strategy. You have experiments.
Where AdviseWell fits
AdviseWell is built around a simple idea:
Advice firms don’t need more AI tools. They need a governed platform where agents can safely run workflows end-to-end.
That’s why AdviseWell is structured like an operating system, not a chatbot:
Capture → Generate → Review → Deliver as one controlled flow
outputs designed to be traceable and verifiable with source links
firm-wide standardisation via templates, tone controls, and hardcoded disclaimers
a review layer that checks for conflicts, inconsistencies, and alignment with ASIC regulations
“agentic control” that lets teams search, add, and update client records and action tasks without living in ten systems
Australian-hosted positioning, with data residency described as Sydney on Google Cloud
an explicit stance that firm data is not used to train third-party AI models
The point is not “AI in advice.”
The point is that agents are becoming part of the workflow whether you like it or not. The firms that win will be the ones who can use them deeply, because they can govern them.
The takeaway
Open agent ecosystems are teaching the world what’s possible.
Advice firms don’t need to wait for open marketplaces to “figure out enterprise security.” They can incorporate the lessons now:
autonomy is coming
clients are already using it
small firms are already rebuilding around it
and bans don’t stop it
So the strategic move is not to debate whether agents are real.
The strategic move is to build an advice-grade environment where agents can operate safely, predictably, and auditably.
That is how AI stops being a novelty and becomes infrastructure.
Share this post:
Discover AdviseWell
Learn more about who we are, what we’re building, and how we’re shaping the future of advice.